Financial controlsOctober 13, 20268 min read
Who Can See Your Financial Records? Run This 30-Minute Access Audit.
Most financial access problems do not begin with a dramatic breach. They begin with an old admin account, a shared password, or a payment change nobody verifies outside the email thread.
A vendor emails a new bank account. The request looks ordinary. The name is right, the invoice is familiar, and the message lands on a busy afternoon. Someone updates the payment details and keeps moving.
That is exactly the kind of moment the IRS called out on October 2 during Cybersecurity Awareness Month. Its reminder was not a new rule. It was a useful operational warning: businesses, payroll teams, and HR staff should watch for phishing, fake invoices, and attempts to steal payroll or W-2 information—and should verify sensitive payment or employee changes through a trusted channel.
For an owner-led business, the practical question is not whether the company has perfect cybersecurity. It is simpler: who can see the financial records, who can change them, who can move money, and how would the team notice if the wrong person tried? A short access audit will not solve every security risk. It can close several of the most avoidable gaps.
A 30-minute financial access audit
Inventory → Tighten → Verify
Inventory
Name the access
Who can get in today?- Account owner and active users
- Roles and administrator rights
- Recovery email and phone
Tighten
Match access to the work
What does each person need?- Individual logins
- Minimum useful permissions
- MFA on sensitive accounts
Verify
Protect the change
How will the team pause?- Trusted-channel callbacks
- Second check for payment changes
- Known recovery contacts
Start with the systems that can expose money or identity
Do not begin with a broad technology inventory. Begin with the short list that would make tomorrow difficult if someone lost control of it: bank and credit-card portals, payroll, cloud accounting, payment processors, merchant accounts, the IRS Business Tax Account, state tax portals, email, password management, and the file storage that holds W-9s, tax returns, payroll reports, or customer records.
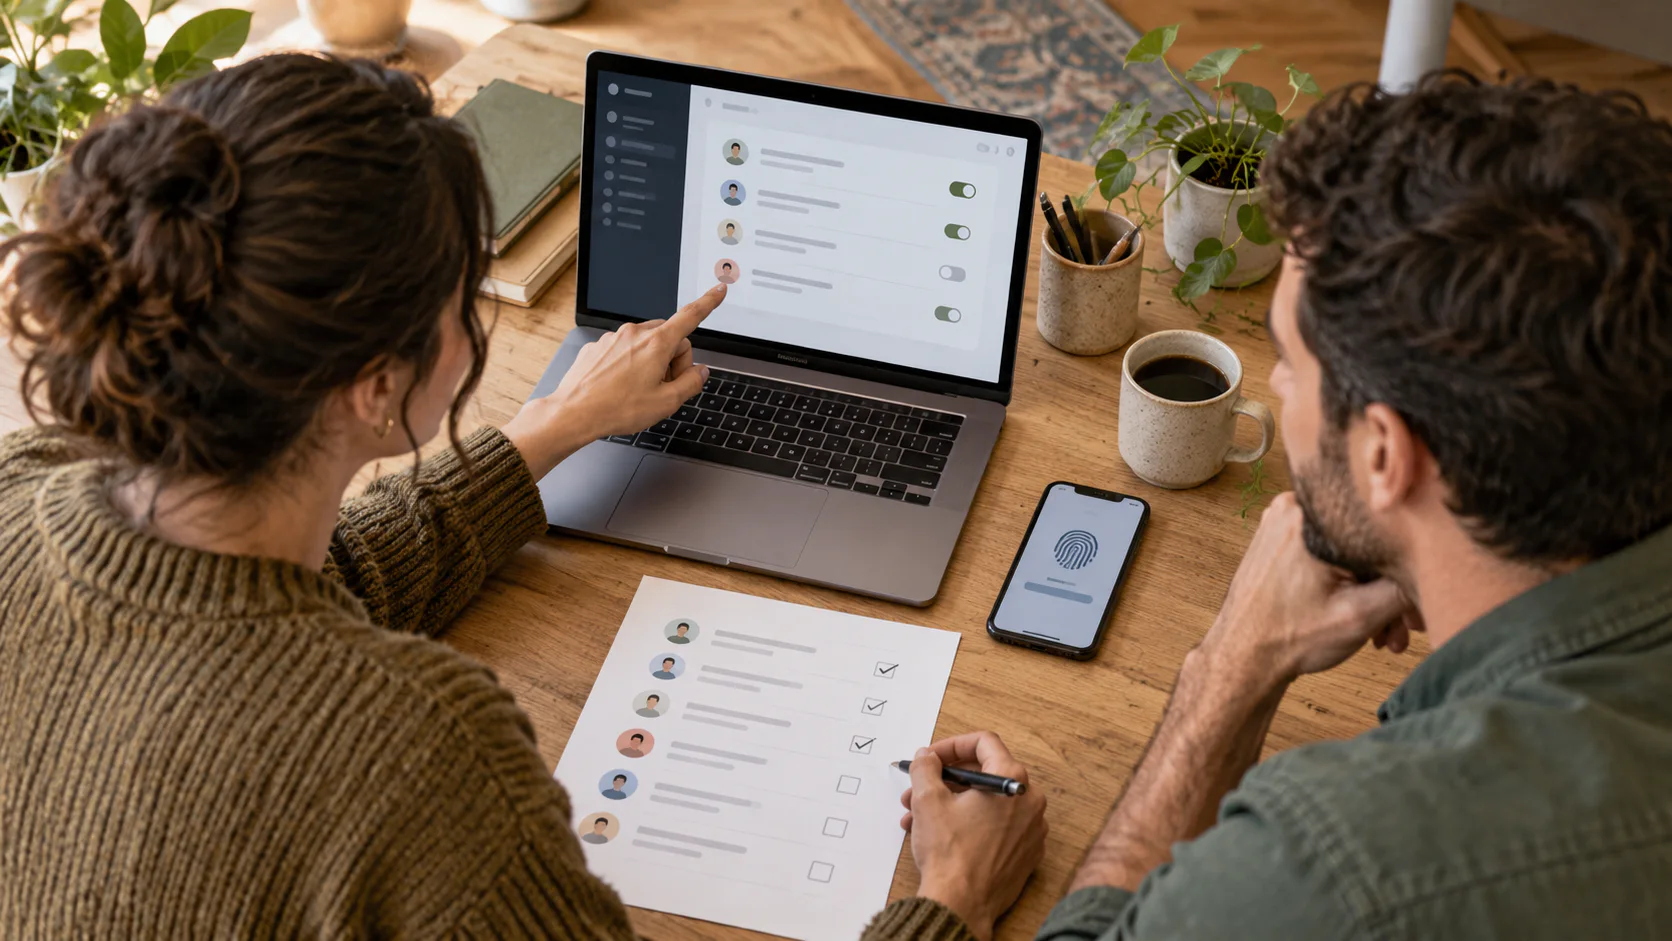
For each system, write down five things: the account owner, every active user, each person’s role, whether multifactor authentication is on, and who controls recovery. Recovery deserves its own column. An account can appear protected while password resets still flow to a former employee’s email or a phone number nobody monitors.
The result does not need to be polished. A one-page list is enough if it answers the question honestly. If the owner cannot tell who has administrator access without opening six apps, the list has already found useful work.
Separate the ability to view, change, approve, and pay
Access is not one permission. A person may need to review a bank balance without being able to send a wire. A bookkeeper may need transaction detail without the authority to add a new bank user. A payroll specialist may need to prepare a payroll run while the owner retains final approval.
Small teams cannot always divide every step among different people, but they can still create a deliberate pause around high-risk changes. A useful minimum is to require a second check before changing vendor bank details, employee direct-deposit information, payroll administrators, or account recovery settings. The reviewer should use a phone number or contact method already on file—not the phone number included in the change request.
Consider a simple example. A project manager regularly approves supplier invoices, so the accounting system correctly gives that person approval access. It does not follow that the same login should be able to edit the supplier’s bank details and release the payment. The right design follows the work. It does not grant every related permission for convenience.
Use controls that a small team can actually maintain
The IRS recommends strong, unique passwords; multifactor authentication; current software; encrypted and backed-up records; secure networks; and caution around urgent messages that request financial information. NIST’s small-business guide puts the same ideas into an approachable order and recommends starting MFA with accounts that hold the most sensitive information.
Translate that guidance into a routine. Turn on MFA for banking, payroll, accounting, tax, merchant, email, and password-manager accounts. Give each person an individual login instead of passing around one credential. Remove access when a role ends. Keep devices and browsers updated. Avoid using public Wi-Fi for financial work. Store sensitive records in an approved location rather than scattering them across inboxes, downloads folders, and personal drives.
Do not overlook email. A compromised inbox can be more useful to a fraudster than a compromised accounting login because it supplies names, timing, invoice patterns, and a believable way to request a change. Protect the email accounts that receive invoices, payroll notices, password resets, and bank alerts with the same care as the financial systems themselves.
A backup is useful only if the business can recover from it
A checked box that says backups are enabled is not the same as a recovery plan. Ask what is backed up, how often, where the copy lives, who can restore it, and whether anyone has tested that process. Cloud software may protect its own service while leaving the business responsible for exported reports, source documents, or records held somewhere else.
Then name the first call if something goes wrong. The owner should not be inventing the response while locked out of payroll on a Friday morning. Keep current contact information for the bank, payroll provider, insurer, technology support, and the professional responsible for tax or accounting work. Legal, contractual, insurance, and notification obligations vary, so an actual incident deserves prompt advice for the facts at hand.
The goal is not to make every owner a security specialist. It is to make access visible, changes deliberate, and recovery possible. Those are financial controls as much as technology controls because they protect the records and authority behind the business’s money.
This week
Make one useful move.
Choose the seven accounts that matter most—banking, payroll, accounting, tax, merchant, email, and file storage. Set a 30-minute timer. For each one, confirm the owner, active users, permission levels, MFA, and recovery contact. Remove stale access, schedule anything that needs technical help, and write one rule: payment and payroll changes are verified through a trusted channel already on file.Sources and further reading
These sources informed the factual framework. The examples and commentary are Honeybee's plain-language interpretation.
- IRS reminder: Cybersecurity Awareness Month offers simple steps to protect tax dataInternal Revenue Service
- NIST Cybersecurity Framework 2.0 for Small BusinessNational Institute of Standards and Technology
- Cybersecurity for Small BusinessFederal Trade Commission
- Creating an account for IRS.govInternal Revenue Service
This article provides general educational information. It is not tax, legal, investment, audit, or attest advice and does not create a client relationship or authorize work.